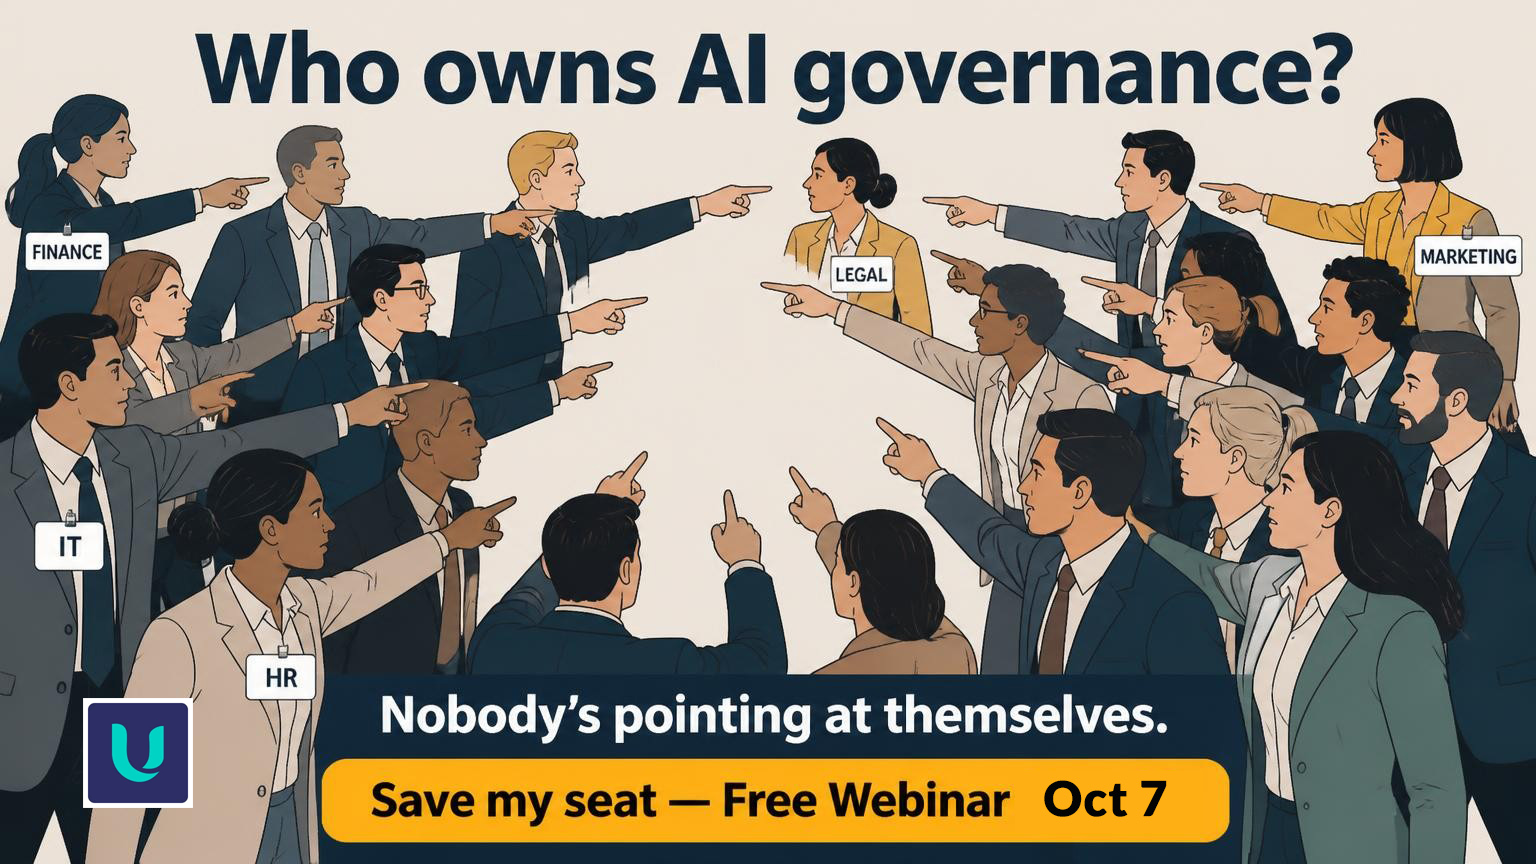
Someone asks "who owns AI governance?" The room goes quiet.
Legal says it's a risk problem. IT says it's a business decision.
The business asks, isn't that what Compliance is for? Four teams, and not one of them says "us."
That quiet is the problem. And it gets more expensive every month it goes unanswered.
AI Governance is different
Here's why AI is different from every rule before it.
Every other rule came through one door and brought a team with it.
SOX went to Finance. HIPAA went to Privacy. PCI DSS went to Payments. One rule, one home, one owner.
AI didn't show up that way.
The tools walked in through HR, marketing, support, engineering, and finance all at once, before anyone picked an owner. No door. No team. No owner.
So here's the shift that ends the argument.
Ownership isn't a job title. It's a list.
Whoever can produce the full list of AI controls your company has to follow, and point to the exact rule behind each one, owns AI governance.
Sort out the list, and the owner gets obvious. Argue about the owner first, and you'll still be arguing next year, with a wider gap than you have today.
Join us On October 7, we're pulling this apart in a free 45-minute session.
You'll walk away with:
- Why AI governance lands on every desk and sticks to none
- How the complete control list actually gets built, and kept right
- A live poll where you see who your peers think should own it
- We'll show how much of that answer sits in the mapping
Our guest is Ulla-Maija Jäske, who runs the Risk Management Office at Fujitsu, a company of about 124,000 people, and led their ServiceNow IRM rollout.
She's been living the "who owns risk" question for years, long before AI muddied it. She shares their AI Governance journey.
45 minutes. Free. Built for CISOs enterprise GRC teams.